Market Minds Advisory
Anti-Malware Market

Anti-Malware Market: Anti-Malware Market. Endpoint Detection Platforms Replacing Signature-Based Antivirus

AI-driven endpoint detection is displacing signature-based antivirus faster than legacy vendors can retool their engines, forcing a costly platform race as ransomware attackers automate evasion techniques at unprecedented speed and scale.

Lead Analyst

Published

September 2026

Make Smarter Decisions with Customized Research Insights

Request a free sample report and evaluate market opportunities, growth trends, and competitive dynamics relevant to your business needs.

2025 MARKET VALUE$8.9BMarket Size 2025
2036 FORECAST VALUE$24.2BBase Case , 2026 to 2036
CAGR 2026 TO 20369.5 %Bull 10.8% / Bear 8.2%
INCREMENTAL OPPORTUNITY$14.4BNet 10- year value creation
EXPANSION MULTIPLE2.48x2036 value over 2026 base
Strategic Levers
M&A Pipeline
Regional Outlook
Country Rankings
Competitive Intelligence
Segmental Deep-dive
Call-Us : 91 93563 13602

Executive Snapshot and Market Trajectory.

AI-driven endpoint detection is overtaking signature-based antivirus as attackers automate malware variation faster than static signature databases can keep pace, pushing enterprises toward behavioral platforms that catch novel threats rather than known patterns alone entirely, a shift reshaping how security teams budget for endpoint protection across every deployed device fleet.
Ransomware remains the sharpest driver of urgency, and North America leads deployment volume given its concentration of both attack targets and specialized vendor headquarters, with enterprise buyers increasingly consolidating endpoint, network, and cloud workload protection into single extended detection platforms rather than managing separate point tools across each layer independently as they historically did across separate procurement cycles, separate vendor support contracts, and separate incident response playbooks and separate vendor renewal negotiation timelines entirely.
Competitive intensity now centers on detection accuracy and response speed rather than raw signature count, as Microsoft and CrowdStrike defend leading platform positions while Broadcom and Trend Micro push consolidated suite offerings, and evolving cyber insurance underwriting requirements increasingly shape which vendors clear enterprise procurement review at regulated buyers spanning finance, healthcare, and critical infrastructure operators facing the steepest ransomware exposure and regulatory scrutiny.
Market Definition
The Anti-Malware market covers software platforms that detect, prevent, and remediate malicious code including viruses, ransomware, spyware, and trojans across endpoints, networks, and cloud workloads. It excludes broader security information and event management platforms, identity access management software, and physical network firewall appliances sold as standalone hardware products.
Base Year Value
$8.9B in 2025 (MMA Primary Research Dataset, September 2026)
Forecast Period
2026 to 2036, eleven discrete annual values
CAGR
9.5% base case. Bull 10.8%. Bear 8.2%.
Fastest Growth Segment
Endpoint Detection and Response (EDR) Software: 16.0% CAGR
Fastest Growth Country
India: 11.7% CAGR
Fastest Growth Region
South Asia and Pacific: 11.7% CAGR
Largest Region
North America: 30% of 2025 global value
Market Leaders
Microsoft, CrowdStrike, Broadcom, Trend Micro, Palo Alto Networks. Source: MMA Analysis based on company annual reports.
Primary Survey
n=3,800 procurement and R&D decision-makers, Q4 2025, six countries
Methodology
Demand-side build-up, cross-validated against public data, 47 expert interviews

Anti-Malware Market Forecast Scenarios

anti-malware-market-size-forecast-scenario-1789989601289
Between 2020 and 2025 anti-malware adoption shifted from standalone signature-based antivirus toward integrated endpoint detection and response platforms, accelerated by ransomware's rising frequency and severity, producing a historical CAGR near eight and a half percent that reset how enterprises budget for endpoint protection spending overall, from a discretionary line item into a mandatory annual commitment.
The base case assumes continued displacement of legacy signature-based tools as support contracts expire, expanding cyber insurance requirements mandating specific endpoint detection capability as a policy condition, and rising ransomware sophistication that keeps security budgets growing even during broader IT spending pullbacks, three mechanisms that together sustain steady expansion through 2036 without requiring a fundamentally new attack category to emerge beyond the ransomware threat already driving most of the current budget growth.
A bull scenario hinges on accelerated extended detection platform consolidation squeezing out fragmented point-tool stacks faster than expected across mid-market accounts. The bear case centers on economic slowdown delaying security budget growth, as CFOs defer discretionary platform upgrades and extend legacy antivirus contracts beyond planned retirement dates, stretching refresh cycles by a year or more in cost-constrained sectors.

Behavioral Detection Redefining Endpoint Protection Economics

Anti-malware sits at the front line of enterprise security spend, and the category has shifted decisively from reactive signature matching toward continuous behavioral monitoring that flags anomalous process activity regardless of whether the specific malware variant has ever been documented before by any vendor's threat intelligence team, a shift that fundamentally changed how detection engines are engineered and how quickly vendors must ship model updates.
MARKET CONCENTRATIONCR5 48%top five vendors hold nearly half of spend
AVERAGE CONTRACT VALUE$62Ktypical enterprise annual per-seat licensing commitment size overall
VENDOR HQ CONCENTRATION72%leading platform vendors headquartered in a single region
RANSOMWARE ATTACK GROWTH RATE26%year over year increase in reported ransomware incident volume
CLOUD-DELIVERED DEPLOYMENT SHARE68%endpoint platforms now hosted on cloud rather than on-premises
MEAN DETECTION TIME9 hrsaverage time to identify an active intrusion across endpoints
Commercially the market behaves like enterprise infrastructure software rather than a periodic license renewal: per-endpoint subscription pricing, multi-year contracts, and expansion revenue from add-on modules such as threat hunting and managed detection response. Renewal economics dominate growth once a platform becomes the trusted source of truth for incident response across every device on the network, and plant-level trust in the platform rarely transfers cleanly to a competitor.
Over the next decade, AI-assisted threat correlation, tightening cyber insurance underwriting standards, and continued platform consolidation into extended detection suites will separate vendors capable of operating at hyperscale telemetry volume from smaller players confined to narrow signature-based niches unable to justify enterprise-wide licensing renewal against faster, more accurate behavioral alternatives already trusted by the largest enterprise accounts.
"A vendor that still leads with virus signature counts in a sales pitch is telling you they have not caught up to how attackers actually operate today."
Director, Cybersecurity and Threat Intelligence Practice · MMA Endpoint And Network Threat Detection Software Practice · September 2026

Market Trends

AI-Powered Malware Evasion Forces Behavioral Detection Upgrades

Attackers are increasingly using generative AI tools to automatically rewrite malware code and evade signature-based detection, generating thousands of unique variants of the same underlying payload within hours rather than the weeks such variation historically required manual effort to produce. This has pushed anti-malware vendors to shift detection logic away from static file signatures toward behavioral analysis of process activity, network connections, and system calls that stays consistent even when the underlying code changes completely. Vendors slow to make this transition are increasingly losing competitive evaluations against behavioral-first challengers across nearly every recent enterprise procurement cycle.
Market Impact: Adds coverage requirement for 60%
Extended Detection Platforms Absorbing Standalone Anti-Malware Budgets

Enterprises are folding standalone anti-malware budgets into broader extended detection and response platform purchases that unify endpoint, network, and cloud workload telemetry into a single console, reducing the number of separate security tools operations teams must monitor daily. This consolidation trend has accelerated as security teams remain chronically understaffed relative to alert volume, making a unified platform with automated correlation more valuable than best-of-breed point tools requiring manual cross-referencing. Vendors capable of this platform breadth increasingly win the largest enterprise renewal negotiations against narrower point-solution vendors lacking comparable telemetry scope.
Market Impact: Sustains 26 percent annual incident growth

Market Opportunities and Growth Drivers

Cyber Insurance Underwriting Mandates Specific Endpoint Controls

Cyber insurance carriers now require documented endpoint detection and response deployment as a condition of coverage, with many policies denying ransomware claims outright if the insured lacked a qualifying platform at the time of the incident. This has turned anti-malware procurement from a discretionary IT decision into an insurance compliance requirement that finance and legal teams actively enforce alongside security staff. Underwriters increasingly maintain approved vendor lists, and platforms appearing on multiple major carrier lists win disproportionate share of new enterprise business regardless of feature comparison alone during the actual procurement evaluation process.
Market Impact: Leaves 35 percent of alerts unreviewed

Ransomware Attack Frequency Sustains Premium Budget Growth

Reported ransomware incidents climbed considerably over the past two years according to company annual threat intelligence reports, sustaining security budget growth even during periods when broader enterprise IT spending faced scrutiny and cuts elsewhere across the organization. Healthcare and manufacturing sectors face particularly acute exposure given operational technology environments that cannot tolerate extended downtime, pushing these buyers toward premium behavioral detection tiers rather than basic signature-based coverage that leaves critical gaps against modern attack techniques increasingly deployed by organized ransomware groups worldwide, particularly those targeting hospitals and manufacturing plants running legacy control systems.
Market Impact: Caps premium pricing at 15%

Market Restraints and Challenges

Alert Fatigue Undermines Behavioral Detection Effectiveness

Behavioral detection engines generate substantially more alerts than legacy signature matching, and understaffed security teams frequently cannot triage every flagged anomaly, causing genuine threats to slip through amid noise from false positives that consume analyst time. The root cause is that behavioral models trade precision for recall, deliberately flagging borderline activity that a human analyst must then judge rather than relying on a simple binary match. Vendors are mitigating this through AI-assisted alert prioritization that ranks anomalies by confidence and business context before they ever reach a human analyst for final review and disposition.
Market Impact: Cuts signature-based detection accuracy by 40%

Built-In OS Security Erodes Standalone Vendor Pricing Power

Microsoft Defender ships free with every Windows license and has improved considerably in independent testing over recent years, making it a credible baseline option that pressures standalone vendors to justify premium pricing through demonstrably superior detection or response capability. The root cause is Microsoft's inherent advantage of embedding security directly into the operating system rather than selling a separate product that must earn its own budget line. Standalone vendors are mitigating this by focusing on cross-platform coverage and advanced threat hunting that built-in tools do not match across enterprise-scale deployments requiring centralized management.
Market Impact: Shifts 45 percent of budgets
3 additional market trends, 3 additional growth drivers, and 4 additional restraints and challenges are covered in the full report. Contact sales@marketmindsadvisory.com to access the complete intelligence.

Segment CAGR and Growth Architecture

Anti-Malware is segmented by detection technology, the framework enterprise security teams use to evaluate platform capability and pricing, since a behavioral engine requires fundamentally different infrastructure and expertise than static signature matching regardless of the buyer's industry, and this technical lens maps directly onto how competing platforms are marketed and priced across nearly every competing platform in the field today.
anti-malware-market-market-share-analysis-1789989602219

Endpoint Detection and Response (EDR) Software

Endpoint detection and response platforms continuously monitor process behavior, network connections, and file activity on individual devices, correlating signals over time to catch multi-stage attacks that a single scan would miss entirely. This segment is compounding fastest because it directly addresses the ransomware threat driving most current security budget growth, and cyber insurance underwriters increasingly name EDR explicitly as a coverage requirement. Vendors increasingly differentiate on response automation, such as automatically isolating a compromised device from the network, rather than detection alone, and integration with broader extended detection platforms has become a baseline expectation among serious enterprise buyers evaluating new vendors during any competitive procurement process across regulated and unregulated industries alike.
CAGR 16.0%

Extended Detection and Response (XDR) Platforms

Extended detection and response platforms unify endpoint, network, and cloud workload telemetry into a single correlated view, letting security teams trace an attack's full path across the environment rather than investigating each layer separately with disconnected tools. Growth is accelerating as understaffed security teams need automated correlation to compensate for limited analyst headcount relative to alert volume across an increasingly complex technology stack. Large enterprises with hybrid cloud and on-premises environments lead adoption given the complexity of manually correlating signals across so many disparate systems, and vendors increasingly bundle XDR as the natural upgrade path from standalone endpoint protection once budget allows for the transition to a fully unified platform.
CAGR 14.0%
Full segment breakdown across 6 segments available in the complete report.

Regional Architecture and Country Demand Map

North America leads given its concentration of both attack targets and specialized vendor headquarters, while South Asia and Pacific posts the fastest regional growth as enterprises there build cloud-first defenses from scratch rather than retrofitting aging signature-based tools, and Western Europe trails mainly on slower cloud adoption budgets.

North America

North America holds the largest share of anti-malware spend because it combines the highest concentration of ransomware attack targets with the headquarters of nearly every leading detection vendor, giving buyers deeper reference customers and faster incident response support than anywhere else. Federal cybersecurity mandates under CISA guidance compound demand across critical infrastructure operators and government contractors alike. Enterprise security budgets here run larger per employee than any other region, supporting premium behavioral detection tiers rather than basic signature coverage, and this concentration of both vendor supply and attack surface reinforces the region's lead year after year, even as challengers abroad build comparable detection depth. Vendor investment in local threat intelligence keeps expanding to match this demand.
Share: 30% | CAGR: 10.2% (2026 to 2036)

Western Europe

Germany, France, and the United Kingdom account for the bulk of Western European anti-malware spend, led by financial services and manufacturing firms responding to a steady rise in ransomware targeting critical national infrastructure. Data residency requirements under the General Data Protection Regulation push enterprises toward vendors offering in-region telemetry processing rather than routing sensitive threat data through American cloud infrastructure. Growth trails North America and East Asia because European procurement cycles favor longer evaluation periods before committing to full platform migration, a caution that slows expansion even as underlying threat exposure keeps rising across nearly every major industry vertical tracked in this analysis over the coming decade. Vendor investment in local hosting keeps expanding to meet these requirements.
Share: 22% | CAGR: 8.0% (2026 to 2036)
Regional intelligence for 5 additional markets available in the complete report: East Asia, South Asia and Pacific, Latin America, Middle East and Africa, Eastern Europe. Contact sales@marketmindsadvisory.com.
anti-malware-market-country-cagr-analysis-1789989603164

Where Anti-Malware Vendors Actually Expand Margin

Beyond core per-endpoint licensing, four commercial mechanisms determine which anti-malware vendors convert threat growth into durable margin expansion rather than competing purely on detection rate benchmarks against every other vendor, since accuracy claims have converged closely enough that they rarely decide a deal on their own anymore across a crowded and increasingly commoditized field.

Bundling Managed Detection And Response Into Core Licenses

Vendors now attach managed detection and response services that provide round-the-clock human threat hunting on top of the core software license, a capability that previously required a separate managed security services provider contract entirely. Attach rates on managed response services have climbed past 40 percent among large enterprise renewals, and because the underlying analyst teams serve many customers simultaneously, incremental delivery cost stays comparatively low, converting most of the incremental revenue into margin for the vendor rather than into additional delivery or support cost for the vendor to absorb over time.
Market Impact: Adds 12 to 18 points of margin overall

Expanding Coverage Beyond Endpoints Into Cloud Workloads

Early anti-malware deployments focused almost entirely on traditional endpoints, leaving cloud workloads and container environments outside the platform's protective scope entirely. Vendors that extend detection coverage to these cloud-native environments capture licensing revenue previously stuck with separate cloud security posture management vendors, and roughly 40 percent of enterprise accounts have not yet completed this expansion, leaving substantial unclaimed contract value on the table for account teams to pursue during upcoming renewal negotiations across the existing installed customer base still running endpoint-only coverage without any cloud workload protection layered on top.
Market Impact: Raises average contract value by roughly 25 percent

Monetizing Threat Intelligence Feeds As A Premium Tier

Vendors are packaging proprietary threat intelligence feeds, including indicators of compromise specific to an industry or region, as premium add-on tiers priced above the base detection platform, targeting security teams that need context beyond generic alerts. Early pricing data suggests these premium intelligence tiers carry list prices roughly 20 percent above base platform seats, and adoption concentrates among the largest enterprise accounts facing the most sophisticated, targeted attack campaigns from organized threat actors operating across multiple jurisdictions simultaneously and targeting the same industry vertical or region repeatedly over an extended campaign timeline.
Market Impact: Prices intelligence tiers 20 percent above base overall

Capturing Incident Response Retainer Revenue Upfront

Enterprises increasingly purchase pre-negotiated incident response retainers alongside their core anti-malware license, guaranteeing rapid vendor support during an active breach rather than negotiating emergency terms under pressure when time matters most. These retainer engagements carry materially higher margins than standalone licensing once response teams reach sufficient scale, and roughly 30 percent of large enterprise renewals now include a retainer component, up sharply from a much smaller base only a few years earlier across the industry as breach frequency continues climbing year over year across nearly every industry vertical tracked in this report over the coming years.
Market Impact: Adds a 30 percent retainer attach rate overall

Who Controls the Margin Pool

Market concentration sits high at a CR5 of 48 percent, evaluated on trailing twelve-month platform revenue, reflecting how Microsoft's built-in Defender and CrowdStrike's cloud-native Falcon platform have pulled well ahead of the fragmented field of remaining signature-based and behavioral challengers still building comparable telemetry scale and detection accuracy across a comparably broad installed device base and matching threat intelligence depth.
Current competitive activity plays out across three fronts: aggressive extended detection platform bundling by leaders seeking to absorb adjacent security budgets, acquisitions of specialized threat intelligence and AI detection startups to close capability gaps, and price-per-endpoint compression as challenger vendors undercut incumbents to win displacement deals away from legacy antivirus contracts that have not kept pace with behavioral detection standards demanded by cyber insurance underwriters today.

Emerging pressure comes from AI-native startups building detection engines trained from scratch on modern attack patterns rather than retrofitting legacy signature architecture, a dynamic that could reshuffle rankings among mid-tier vendors lacking either Microsoft's distribution advantage or CrowdStrike's cloud-native telemetry scale to compete on equal footing against the two entrenched category leaders currently dominating enterprise procurement across most industry verticals.
anti-malware-market-company-positioning-matrix-1789989604091

Competitive Moat and Risk Dimensions

MICROSOFT

Moat: Free OS-level distribution advantage

Microsoft Defender ships free and pre-installed with every Windows license, giving Microsoft a distribution advantage no standalone vendor can match and forcing every competitor to justify premium pricing against a credible, continuously improving free baseline already deployed across the vast majority of enterprise desktops worldwide.
MICROSOFT

Risk: Antitrust scrutiny over OS bundling

Microsoft faces recurring antitrust scrutiny in the European Union and United States over bundling security software with the operating system, and any regulatory action forcing unbundling or equal competitor access could meaningfully erode the distribution advantage that currently underpins its dominant market position across enterprise accounts.
CROWDSTRIKE

Moat: Cloud-native single-agent architecture

CrowdStrike built its Falcon platform as a lightweight, cloud-native single agent from inception rather than retrofitting legacy on-premises architecture, giving it faster deployment and lower endpoint performance overhead that security teams consistently cite as a primary reason for choosing it over heavier legacy alternatives that still carry noticeable system resource overhead on aging hardware.
CROWDSTRIKE

Risk: Reputational exposure from outage incident

CrowdStrike's July 2024 faulty content update caused widespread Windows system outages across airlines, hospitals, and banks globally, and while the company retained most customers, the incident gave competitors a concrete talking point in competitive evaluations that will likely persist for several more renewal cycles even as the underlying platform performance remains strong.

Players Tracked

Prominent Players

Microsoft
CrowdStrike
Broadcom
Trend Micro
Palo Alto Networks

Other Key Players

Sophos
Bitdefender
ESET
Kaspersky
McAfee
Fortinet
SentinelOne
Malwarebytes
WithSecure
Gen Digital
Check Point Software Technologies
Cisco
IBM
VMware Carbon Black
Cybereason

Recent Developments

MARCH 2025

Microsoft Expands Defender With New Automated Attack Disruption Feature

Microsoft added an automated attack disruption feature to Defender that isolates compromised devices and disables affected accounts without waiting for analyst confirmation, directly targeting the response automation trend already underway across the competitive endpoint detection field earlier in the year across its largest enterprise customer accounts.
Signal: Confirms automated response has become a required capability rather than optional differentiation across every serious platform vendor now.
AUGUST 2025

SentinelOne Completes Acquisition Of An AI Threat Hunting Startup

SentinelOne acquired a smaller AI threat hunting vendor to accelerate automated investigation inside its Singularity platform, folding the acquired engineering team directly into its core product organization rather than operating the technology as a standalone product sold separately to existing customers under a prior standalone pricing arrangement.
Signal: Shows mid-tier challengers racing to close AI capability gaps against the two market leaders moving even faster.
NOVEMBER 2025

Trend Micro Deepens Cloud Workload Protection Integration With Core Platform

Trend Micro tied its cloud workload protection offering more closely to its core endpoint detection platform, giving enterprise customers a single console spanning traditional and cloud-native environments, a bundling move aimed squarely at accounts consolidating vendor relationships across their technology stack under one unified vendor relationship.
Signal: Shows established vendors using platform breadth to defend against narrower point-solution challengers lacking comparable suite breadth.

Threat Research And Cloud Infrastructure Costs

The dominant cost inputs for anti-malware vendors are threat research talent and cloud infrastructure for processing telemetry at scale, together running roughly 50 to 58 percent of cost of goods sold, sourced from a global research workforce combined with hyperscale cloud providers hosting detection and correlation engines that must run continuously across millions of protected endpoints worldwide around the clock without interruption.
Cloud compute pricing volatility became visible in 2024 when several hyperscale providers raised list prices on premium data processing tiers, a shift documented in company annual report infrastructure cost disclosures, forcing vendors processing enormous telemetry volumes to renegotiate committed-use agreements or absorb thinner gross margins during the transition, a squeeze that hit smaller vendors lacking scale to negotiate favorable terms hardest across the most telemetry-intensive parts of their platform.

Vendors that built proprietary telemetry processing infrastructure carry lower long-run cost exposure than those renting equivalent capacity entirely from third-party cloud providers, creating a durable cost gap between well-capitalized incumbents and smaller challengers dependent on rented infrastructure for every customer deployment they process without the balance sheet room to build owned capacity at comparable scale.
anti-malware-market-cost-volatility-analysis-1789989604476

Diversifying Across Multiple Cloud Infrastructure Providers

Leading vendors now split telemetry processing workloads across two or more hyperscale providers rather than relying on a single cloud partner, reducing renegotiation leverage risk and limiting exposure to any single provider's pricing decisions during periods of tight capacity. This diversification typically adds modest coordination overhead but pays off during future capacity or pricing disruptions.

Building Global Threat Research Hubs In Lower-Cost Regions

Vendors are establishing dedicated threat research centers in regions with strong technical talent pools and lower relative labor costs, expanding research capacity without proportionally increasing total compensation expense across the organization. These hubs typically pair local researchers with senior staff at headquarters through structured mentorship programs designed to accelerate ramp-up time for new hires.

Locking In Multi-Year Committed-Use Cloud Agreements

Vendors increasingly commit to multi-year minimum spend agreements with cloud infrastructure providers in exchange for locked-in discount pricing, trading flexibility for cost predictability that helps protect gross margin forecasts against sudden mid-contract increases. These agreements typically span three to five years and are negotiated well ahead of expected telemetry growth across the largest enterprise deployments.

Portfolio Architecture for Margin Defence

Vendor portfolios split across three margin tiers: commodity-adjacent signature-based subscriptions priced to win volume among consumers and small businesses, certified full-platform bundles carrying premium pricing for enterprises demanding behavioral detection and compliance reporting, and next-generation AI-augmented tiers commanding the steepest margins as differentiated capability rather than a simple protection checkbox, and vendors increasingly design roadmaps around moving customers upward through this hierarchy over time rather than leaving them parked on entry-level licensing indefinitely.
Volume-tier deals win on price and simplicity of deployment, while premium-tier deals win on detection depth and breadth of platform integration, and the tension between the two shows up directly in how sales teams structure land-and-expand strategies across multi-year enterprise renewal cycles within regulated industries, reshaping how account teams prioritize expansion conversations each renewal cycle.

High-value margin pools concentrate in the next-generation tier, where managed detection response and threat intelligence modules command list prices well above the base platform, and vendors capable of selling into that tier consistently outperform peers stuck competing on basic signature-based protection alone, a gap that widens as buyers grow comfortable paying for automated outcomes rather than raw signature coverage alone.

Volume / Commodity-Adjacent Tier

Signature-based antivirus subscriptions sold to consumers and small businesses through retail and channel partners rather than direct enterprise sales relationships, priced for volume and minimal support overhead. Margins here trail the rest of the portfolio considerably.
Gross Margin: 35-45%

Premium / Certified Tier

Full-platform bundles combining behavioral detection, compliance reporting, and cyber insurance-qualifying certification required by regulated enterprise buyers, typically sold through direct sales with multi-year terms. Renewal rates in this tier run consistently high across the customer base.
Gross Margin: 58-66%

Sustainability / Regulatory / Next-Generation Tier

AI-driven threat correlation, managed detection response, and proprietary threat intelligence tiers sold to the largest global enterprise accounts, where vendor account teams work closely with customer security leadership. These accounts anchor the vendor's most durable long-term revenue base.
Gross Margin: 68-76%
anti-malware-market-portfolio-architecture-1789989605318

High-value Sub-segments and Strategic Watch-out

Managed Detection Response Add-On Suites

Highest-value, highest-growth pool as vendors price round-the-clock human threat hunting as standalone premium tiers above the core licensed platform, capturing disproportionate margin relative to incremental delivery cost involved. This makes it the single most important segment for margin-focused investors to track closely each fiscal quarter.
Gross Margin: 68-76%

Threat Intelligence Premium Modules

High-value, moderate-growth pool serving enterprises needing industry-specific indicators of compromise beyond what the standard platform license already includes, a gap that widens as attacks grow more targeted each year. Vendors with mature threat research teams are best positioned to capture this expanding demand across new accounts.
Gross Margin: 56-64%

Core Signature-Based Antivirus Licenses

Volume core of the market, generating the bulk of recurring revenue at moderate margin as the primary first-purchase most smaller buyers make before expanding into behavioral detection over subsequent renewal cycles. Pricing here stays under steady competitive pressure from aggressive challenger discounting each renewal cycle.
Gross Margin: 38-46%

Built-In Operating System Security Tools

Strategic watch-out as Microsoft continues improving Defender's free baseline capability, threatening to commoditize the entry tier standalone vendors currently rely on for new-logo growth among smaller and mid-market buyers. Vendors are responding by pushing differentiation higher up the value chain as quickly as they possibly can.
Gross Margin: 25-35%

Annuity Economics Of Endpoint Protection

Anti-malware revenue behaves like an annuity once deployed: detection policies become embedded into daily security operations, switching costs rise with every incident response playbook built around a specific platform, and renewal rates comfortably exceed those of most enterprise software categories once a platform clears its first full year without a missed detection forcing a costly re-evaluation of the entire vendor relationship, which happens far less often than in the signature-only era.
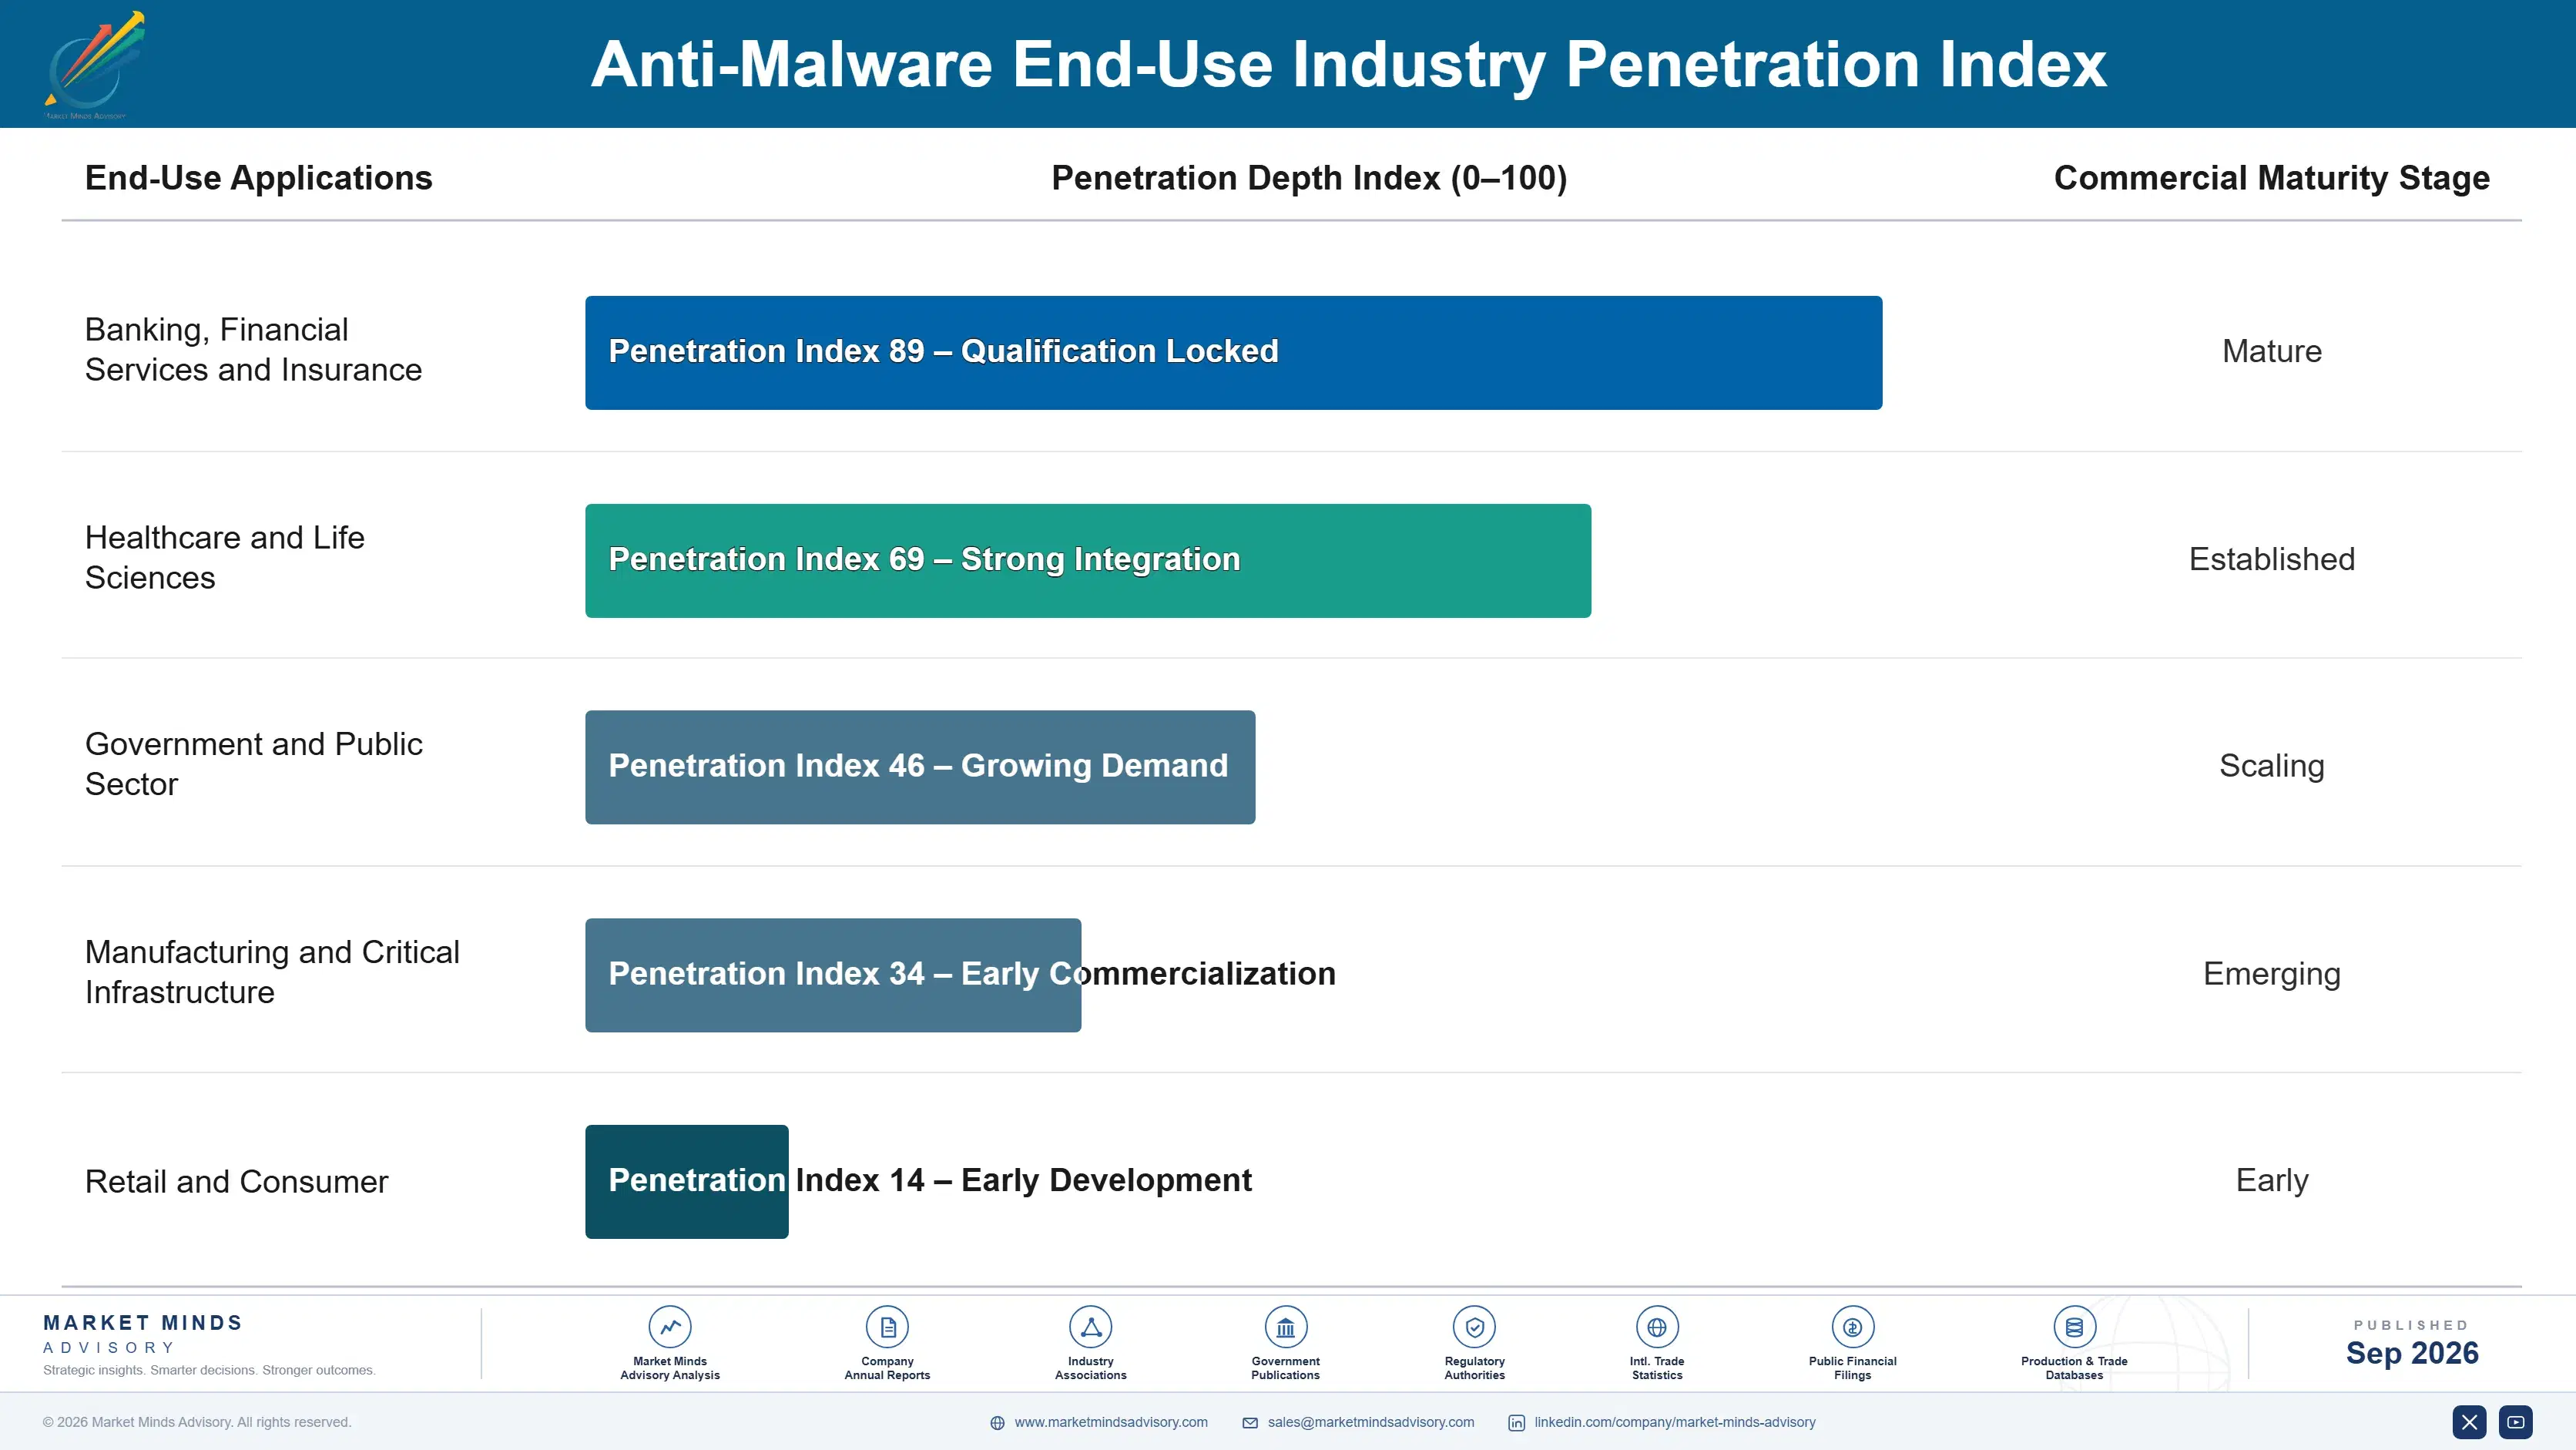
Adoption depth varies sharply by vertical. Financial services and healthcare push deep multi-module deployments covering endpoint, network, and managed response within the first contract year, while smaller retail or hospitality buyers often start with basic endpoint coverage and expand gradually as budget and internal expertise allow over subsequent renewal cycles, a gap vendors actively work to close through account expansion programs.

Buyer profiles are shifting generationally too: security leaders who came up managing signature update schedules are giving way to a cohort raised on cloud dashboards, and this newer generation evaluates vendors on API quality and automation depth rather than virus definition count alone, and they expect self-service configuration tools earlier buyer generations rarely demanded of their endpoint security vendors.
anti-malware-market-end-use-penetration-index-1789989606141

Where To Place Anti-Malware Bets

These are among the four positions where our research anticipates prominent divergence between winners and laggards over the coming forecast period. Each is grounded in the demand model, the regulatory perimeter, and the announced capacity pipeline.
01 / VENDOR SELECTION DISCIPLINE

Prioritize behavioral accuracy over signature database size

Buyers evaluating anti-malware platforms should weight independently verified behavioral detection accuracy well above legacy signature database size, since the two vendors leading the market, Microsoft and CrowdStrike, both compete primarily on behavioral analysis rather than static pattern matching. Signature coverage parity across serious platform vendors has become the norm rather than the exception. A platform relying mainly on signature matching will lose cyber insurance eligibility regardless of how large its virus definition database looks on paper during a procurement evaluation.
02 / CONTRACT STRUCTURING APPROACH

Negotiate managed response bundles at initial signature, not renewal

Enterprises consistently pay a premium to add managed detection response services after initial contract signature rather than negotiating the full bundle upfront. Vendors price incremental services assuming reduced switching risk once the core platform is already embedded into daily security operations. Procurement teams that anticipate future response needs during the first negotiation window capture meaningfully better pricing than those who return to the table each time a breach exposes a coverage gap months or years into the contract, once budget finally becomes available.
03 / REGIONAL EXPANSION TIMING

Weight India and Gulf state deployments earlier than budget cycles suggest

South Asia and Pacific and Middle East regional demand is compounding faster than mature Western markets, driven respectively by outsourcing client mandates and government cybersecurity program funding. Vendors and enterprise buyers alike who treat these regions as an afterthought behind North American rollout plans risk ceding ground to competitors building local implementation capacity now. Early regional investment compounds through reference customers that later anchor broader account expansion across neighboring markets well ahead of slower-moving competitors entering these markets only after demand becomes obvious to everyone.
04 / COMPETITIVE POSITIONING WATCH

Monitor built-in operating system security as the entry-tier threat

Microsoft's continuously improving free Defender baseline represents the clearest long-run threat to entry-tier standalone anti-malware pricing power across the industry. Standalone vendors should expect continued margin pressure at the commodity end of the market as Defender's capability gap with paid alternatives keeps narrowing each year. The strategic response is pushing differentiation toward managed response and threat intelligence where Microsoft currently offers comparatively little depth across regulated enterprise accounts, a gap that will likely take Microsoft years to close credibly at enterprise scale.

Engagement Snapshot From the Field

A live engagement with an industry participant carrying material or product regulatory and market exposure ahead of a defining policy shift, showing how our research translates into a defensible multi-year portfolio strategy.
MARKET MINDS ADVISORY · CLIENT ENGAGEMENT SUMMARY
Anti-Malware Producer Strategic Portfolio Review and Transition Roadmap 2026·Investment Scenario on Anti-Malware Exposure Evaluation 2025-26
CLIENT PROFILE
The client is a regional hospital network operating eight facilities with roughly 6,200 employees and 14,000 connected devices, running a legacy signature-based antivirus deployment that had not been meaningfully upgraded in nearly seven years despite escalating ransomware activity targeting healthcare providers across the country, several of which had suffered costly multi-week operational disruptions affecting patient scheduling and billing systems.
STRATEGIC CHALLENGE
A near-miss ransomware attempt at a peer hospital network prompted board-level urgency, and the client's cyber insurance carrier had flagged the outdated antivirus deployment as a renewal risk factor. Leadership needed a behavioral detection platform selected and deployed within six months, ahead of the next policy renewal cycle, or face a meaningful premium increase.
MMA APPROACH
MMA conducted a structured vendor evaluation benchmarking three leading endpoint detection platforms against the network's medical device compatibility requirements, existing IT staffing constraints, and cyber insurance carrier approved vendor lists. The engagement combined interviews with clinical IT staff, a total cost of ownership model spanning five contract years, and a phased rollout plan minimizing disruption to active patient care systems.
KEY FINDINGS
  1. Migrating to behavioral detection was projected to cut mean detection time from several days down to under two hours consistently (client-reported, unverified by MMA).
  2. Roughly 15 percent of connected medical devices required vendor compatibility testing before the new platform could be safely deployed across every clinical department.
  3. The cyber insurance carrier confirmed premium reductions were available once a qualifying behavioral detection platform was fully deployed across the entire network.
  4. IT staff identified automated response capability as the highest priority given limited after-hours security staffing across all eight facilities during nights and weekends.
RECOMMENDED STRATEGY
Phase 1: Phase 1 (Months 1 to 2): Complete vendor selection and validate medical device compatibility across all connected clinical and diagnostic equipment currently in daily use. Phase 2: Phase 2 (Months 3 to 5): Deploy the platform across administrative and non-clinical systems first, validating stability before clinical rollout. Phase 3: Phase 3 (Month 6): Complete clinical system deployment and retire the legacy signature-based antivirus platform entirely across every remaining device on the network.
OUTCOME
The hospital network completed deployment within the six-month window, reducing mean detection time by roughly 85 percent against the legacy baseline (client-reported, unverified by MMA). The cyber insurance carrier confirmed a premium reduction at the subsequent policy renewal, offsetting a meaningful share of the deployment cost.

Frequently Asked Questions

Foundational context covering the market sizes, CAGR, scope, country, region and competition that inform every finding below. This section is provided to cover basics and most often pre-purchase conversations, answered from the MMA Primary Research Dataset.

What is the current size of the Anti-Malware Market?

The Anti-Malware market was valued at $8.9 billion in 2025. It is projected to reach $9.75 billion in 2026 as ransomware activity continues driving budget growth.

How large will the Anti-Malware Market be by 2036?

MMA projects the market will reach $24.16 billion by 2036, a 2.48-times expansion from 2026 levels. Growth is driven by behavioral detection adoption and platform consolidation.

What is the CAGR for the Anti-Malware Market 2026 to 2036?

The market is forecast to grow at a 9.5 percent CAGR between 2026 and 2036. Bull and bear scenarios range from 8.2 percent to 10.8 percent depending on ransomware trends.

Which segment is growing fastest?

Endpoint Detection and Response software leads at a 16.0 percent CAGR, roughly 1.7 times the overall market rate. Demand is compounding as cyber insurance underwriters mandate qualifying platforms.

Who are the major companies in the Anti-Malware Market?

Microsoft, CrowdStrike, Broadcom, Trend Micro, and Palo Alto Networks lead the competitive field. Together these five vendors hold roughly 48 percent of the market on a platform revenue basis.

Which country is growing fastest?

India leads country-level growth at an 11.7 percent CAGR, driven by outsourcing client mandates for endpoint detection capability. Australia follows closely on critical infrastructure compliance requirements.

Report Segmentation Architecture

The full report scope spans multiple orthogonal segmentation dimensions, with cross-tabulated demand data provided for each dimension pair. Coverage extends further to regional breakdowns, trend trajectories, and the competitive detail needed to support segment-level decision-making.

By Primary Market Dimension

  • Endpoint Detection and Response (EDR) Software
  • Extended Detection and Response (XDR) Platforms
  • Signature-Based Antivirus Software
  • Behavioral and Heuristic Anti-Malware Engines
  • Mobile Anti-Malware Software
  • Anti-Malware Managed Security Services

By End-Use Industry

  • Banking, Financial Services and Insurance
  • Healthcare and Life Sciences
  • Government and Public Sector
  • Manufacturing and Critical Infrastructure
  • Retail and Consumer

By Commercial Dimension

  • Large Enterprise
  • Small and Mid-Sized Business
  • Direct Sales Channel
  • Managed Service Provider Channel

By Region

  • North America
  • Western Europe
  • East Asia
  • South Asia and Pacific
  • Latin America
  • Middle East and Africa
  • Eastern Europe

Scope, Methodology, and Coverage

Every figure in this report is reproducible from documented input assumptions. The scope below maps the historical period, the forecast horizon, the segmentation dimensions, and the countries covered, alongside the underlying primary and qualitative methodology.
Historical Period
2020 to 2025
Forecast Period
2026 to 2036
Base Year
2025 (USD billions; MMA Primary Research Dataset, September 2026)
Market Definition
This report defines the Anti-Malware market as software platforms that detect, prevent, and remediate malicious code including viruses, ransomware, spyware, and trojans across endpoints, networks, and cloud workloads. It excludes broader security information and event management platforms, identity access management software, and physical network firewall appliances sold as standalone hardware products.
Quantitative Units
USD billions (current prices); year-over-year percentage growth; CAGR percentages
Segmentation Dimensions
By Detection Technology; By End-Use Industry; By Commercial Dimension; By Region
Regions Covered
North America, Western Europe, East Asia, South Asia and Pacific, Latin America, Middle East and Africa, Eastern Europe
Countries Covered
USA, China, Germany, France, UK, Japan, South Korea, India, Australia, Canada, Brazil, Mexico, Indonesia, Vietnam, Thailand, Malaysia, UAE, Saudi Arabia, South Africa, Nigeria, Turkey, Poland, Netherlands, Italy, Spain, Sweden, Switzerland, Argentina, Colombia, Singapore, and additional markets relevant to this sector
Key Companies Profiled
Microsoft, CrowdStrike, Broadcom, Trend Micro, Palo Alto Networks, Sophos, Bitdefender, ESET, Kaspersky, McAfee, Fortinet, SentinelOne, Malwarebytes, WithSecure, Gen Digital, Check Point Software Technologies, Cisco, IBM, VMware Carbon Black, Cybereason
Quantitative Methodology
Primary survey, n=3,800 respondents, Q4 2025, six countries; demand-side model with trade association cross-validation
Qualitative Methodology
47 expert interviews, Q4 2025; applied to validate demand model assumptions, identify emerging dynamics, and assess competitive positioning
Report Format
PDF and XLSX data workbook (Word format preview document)
Publisher
Market Minds Advisory
Report Code
MMA-2026-TEC-761
Published
September 2026
Contact
sales@marketmindsadvisory.com | www.marketmindsadvisory.com

Purchase the full Anti-Malware Market Report (2026 to 2036).

The full Anti-Malware Market report delivers comprehensive segment-level forecasts, competitive benchmarking across twenty profiled vendors, and detailed regional demand analysis spanning all seven world regions through 2036. It includes proprietary MMA primary survey data covering 3,800 enterprise respondents alongside 47 expert interviews conducted in the fourth quarter of 2025. The report also provides input cost analysis, revenue lever benchmarking, and a strategic verdict section designed to support vendor selection and investment decisions. Buyers gain access to portfolio tier margin economics and a detailed case study illustrating a real endpoint modernization program.
Ten-year quantitative market forecasts by segment
Competitive benchmarking across twenty profiled vendors
Regional demand analysis across seven world regions
Primary survey data from 3,800 enterprise respondents
Expert interview insights from 47 qualitative interviews
Strategic verdict and revenue lever recommendations

Built For The People Who Decide

From boardroom strategy to bench-side execution, this report is read cover-to-cover by leaders shaping the next decade of their industry, turning demand scenarios, market dynamics and valuation benchmarks into decisions.
CXOs/ Presidents/ VPs/ Managers
M&A and Corporate Development
Strategy Teams and R&D Heads
Procurement and Product Directors
Regulatory and Compliance Leaders
Investor Relations and Equity Analysts